Enterprise-grade multi-engine malware detection, on your infrastructure, and under your control
Every anti-malware engine has a detection gap. When a single engine misses a threat, and they all do (sooner or later), there is no fallback. Cloud-based multi-engine alternatives close that gap, but at a cost: your clients' files transit an offshore platform you don't own, operate, or fully control.
TriDefender is the third option. Multiple independent scanning engines run in parallel, inside your own infrastructure, and return a policy-driven verdict in milliseconds. Nothing leaves your network, ever.
- No files leave your network.
- No black-box software in your environment.
- No per-scan billing at volume.
The governance case
For organisations operating under POPIA, GDPR (or sector-specific data handling obligations) routing file content through a third-party cloud scanning service is a governance nightmare. Vendor contractual assurances do not change the data flow, your clients' content still moves through infrastructure you do not control, to a jurisdiction that may not be your own.
TriDefender eliminates that exposure by design. Every scan is processed on your infrastructure, within your jurisdiction. The data never moves.
How it works
TriDefender integrates into your existing security stack via ICAP, the protocol spoken natively by email servers and secure web gateways. If your appliance already has ICAP support, TriDefender drops into your scanning path without any architectural changes.
When content arrives for scanning:
- Your gateway forwards the payload to TriDefender
- TriDefender fans the payload out to all configured engines simultaneously
- Each engine returns an independent verdict
- TriDefender applies your configured consensus policy and returns a single decision
- Your gateway allows or blocks the content and the full round-trip is measured in milliseconds
Consensus policies let you tune the security/availability trade-off for your environment:
- Union: Block on any detection (the maximum security posture)
- Majority: Block when > 50% of engines agree (balanced coverage with lower false-positive risk), or
- Strict: Block only on unanimous detection ( best for high-availability critical environments
Failure policy governs what happens when an engine is unreachable or times out:
- fail-block: security-first, or
- fail-pass (availability-first).
Hard per-engine connect and read timeouts ensure a degraded upstream scanner can never stall your traffic.
Built for production operations
TriDefender is written in C and was designed to run without operational intervention under normal production conditions.
- Hot configuration reload: Policy and engine changes are applied live via
SIGHUP. No restart, no interrupted connections, no downtime - Hard timeouts at every layer: Per-engine connect and read timeouts, plus a global per-request deadline, prevent any single degraded engine from blocking the request path
- JSON health endpoint: Exposes service status, uptime, active connection count, and queue depth via a UNIX socket. Queryable by any monitoring system
- JSON statistics endpoint: Per-engine request count, success rate, and latency (minimum, average, maximum in milliseconds) via a second UNIX socket. Ready for Prometheus, StatsD, Nagios or Zabbix
- Connection limiting: Configurable maximum concurrent connections; requests beyond the limit receive a clean
503 Service Unavailable - Horizontal scaling: Each instance is fully stateless. Deploy multiple instances behind HAProxy or any load balancer. Reference capacity: approximately 150–200 ICAP requests per second on an 8-core instance, scaling linearly with cores and worker threads
- Syslog integration: All significant events and decisions are emitted via syslog, compatible with any log aggregation or SIEM platform
Visibility and reporting
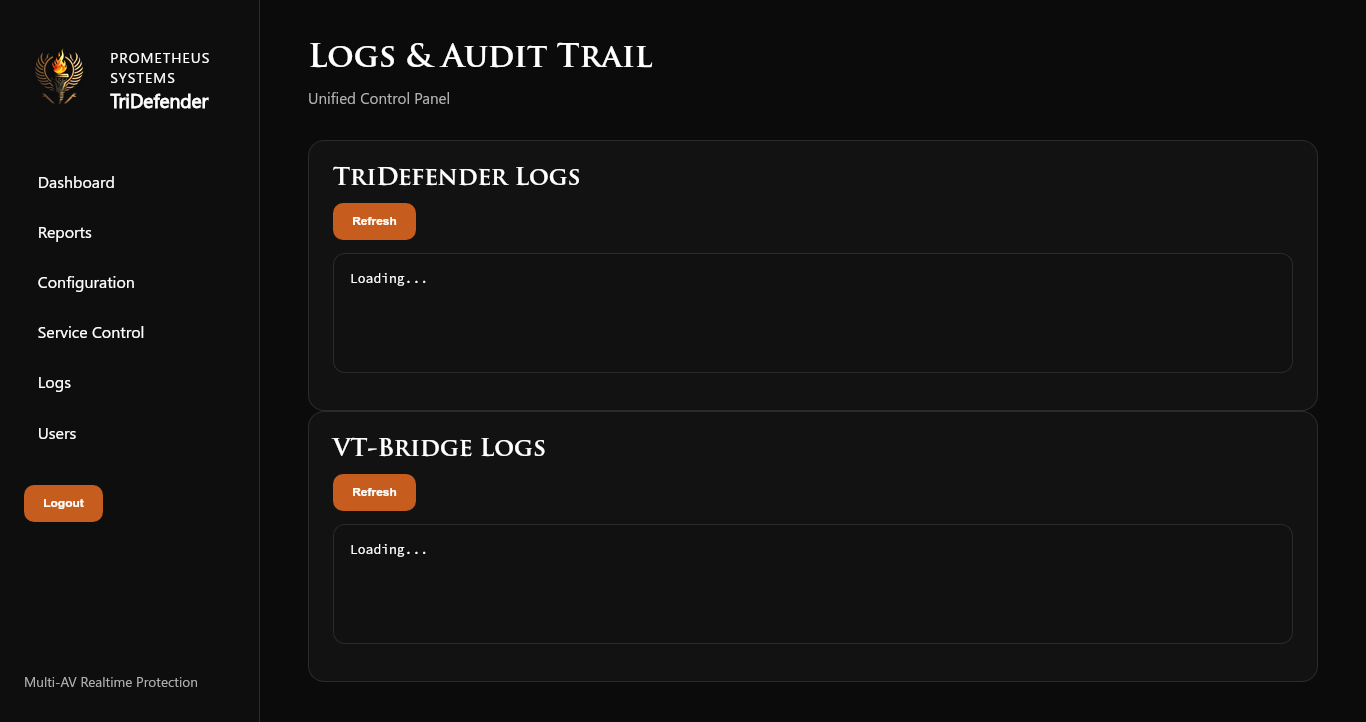
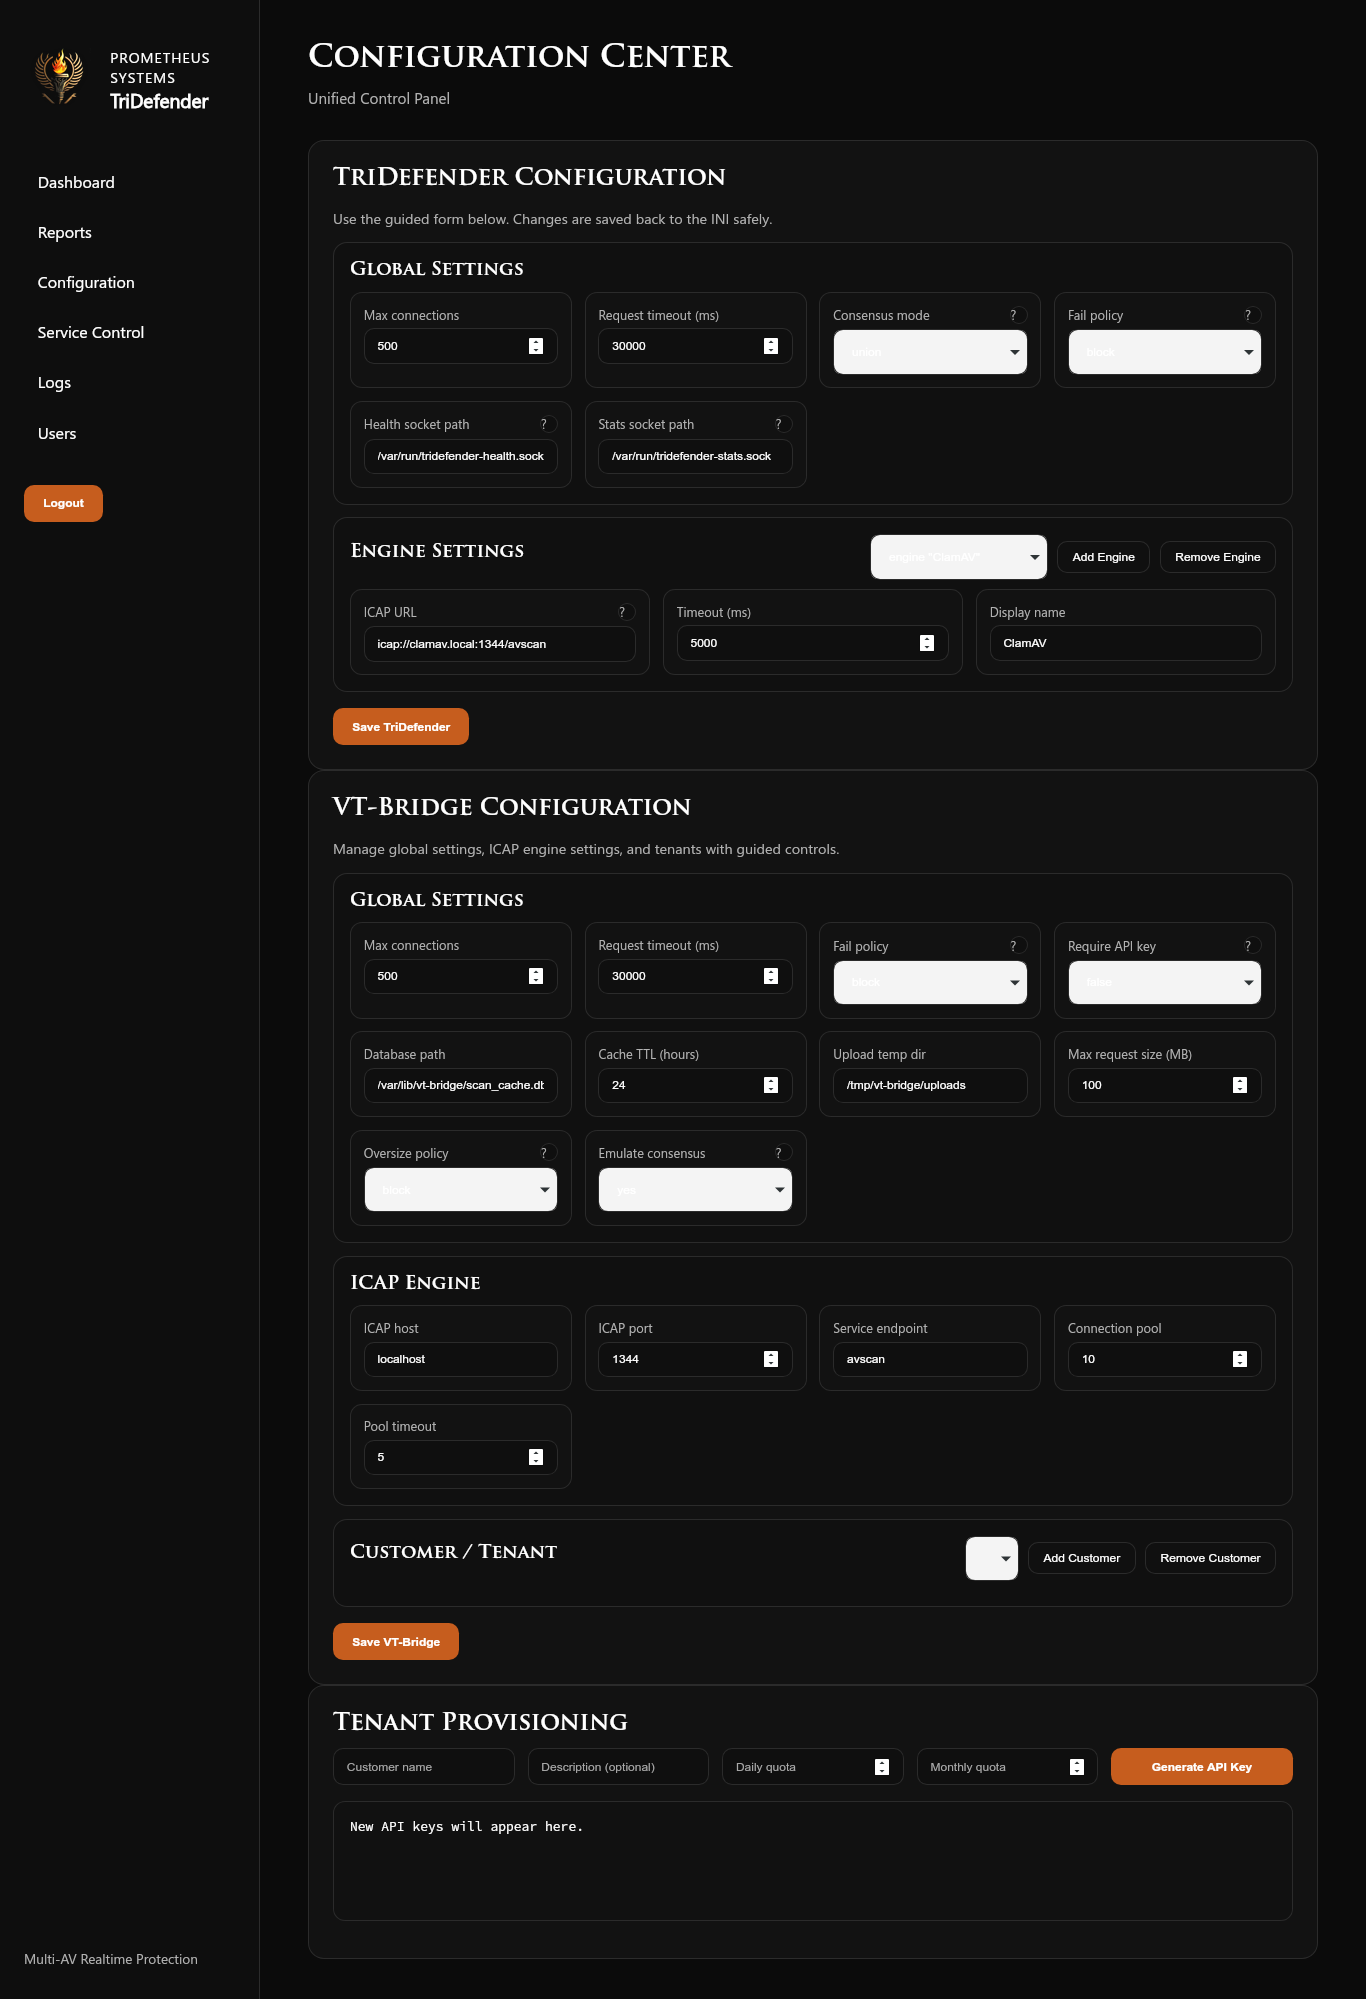
The web control panel provides full operational visibility across both TriDefender and VT-Bridge from a single browser interface: live threat scan volume, per-engine detection rates, cache hit ratios, and a unified audit log across both services. Administrators can start and stop either daemon, manage access credentials, and review the full audit trail of all administrative actions, all without touching the command line.
VT-Bridge: on-premises VirusTotal API compatibility
Many enterprise security platforms, SIEMs, XDR solutions, SOAR platforms, file integrity monitors, etc. are built to make use of the VirusTotal API. For organisations that cannot use VirusTotal due to data sovereignty requirements, cost at scale, or air-gap constraints, VT-Bridge provides a drop-in replacement.
VT-Bridge is a companion daemon that presents a VirusTotal API v3-compatible interface and fulfils every request using your on-premises ICAP scanning infrastructure. It is a clean-room implementation developed solely from VirusTotal's public API documentation, no proprietary code, no reverse engineering.
From your security platform's perspective, it is calling VirusTotal. but every file stays on your network.
VT-Bridge adds:
- Multi-tenant API key management: with configurable per-tenant quotas, designed for MSPs managing multiple client environments from a single deployment
- Result caching: to eliminate redundant scanning of previously seen files, and
- Wazuh FIM compatibility: response formatting matched to Wazuh File Integrity Monitoring's threat intelligence scoring expectations
The combined deployment: TriDefender provides real, parallel multi-engine scanning. VT-Bridge provides the API contract your security ecosystem already expects. Together they deliver on-premises capability functionally equivalent to a VirusTotal Enterprise subscription, at a fraction of the recurring cost, with complete data sovereignty.
Fits your existing stack
TriDefender does not require replacing any existing infrastructure:
- Platform: Enterprise Linux (RHEL 9/10, SUSE SLES, or compatible derivatives) or FreeBSD 14/15
- Scanning engines: Any ICAP-capable scanner, ClamAV, ESET, Sophos, Kaspersky, Symantec, Bitdefender, or any other vendor that exposes an ICAP gateway
- Integration point: Any ICAP-capable proxy or gateway (Squid, nginx, Fortinet FortiGate, BlueCoat, and others)
- Configuration: A single INI file at
/etc/tridefender.ini. No database, no configuration service, no external dependency at runtime or our web UI
If your appliance already speaks ICAP, the integration is a single configuration stanza and a process start.
Licensing and source access
TriDefender is licensed under an annual Code Access Licence (CAL). There are no black-box components, clients receive:
- Access to our package repositories: providing simple deployment via
dnf,zypperorpkg - Full source code: which they can read, build, and audit.
- Support which is contracted separately, based on you're exact needs. The CAL covers all software updates released during the license period.
This has a practical consequence for security-conscious organisations: your team can verify exactly what is running in your environment. There are no undocumented network calls, no silent update mechanisms, and no dependency on Prometheus Systems infrastructure at runtime. The software is entirely self-contained.
Pricing is scaled to the deployment. Reseller and white-label arrangements for ICT consulting firms and managed security providers are open for discussion.
| Feature / Requirement | TriDefender (Air-Gapped On-Prem) | VirusTotal / OPSWAT Cloud |
|---|---|---|
| Data Privacy and Compliance | 100% on-prem, no sensitive data leaves your environment; fully audit-ready | Files transmitted to third-party servers; not suitable for regulated production data |
| Inline Production Scanning | Fully supported, integrates via ICAP with mail gateways, file servers, proxies | Limited; intended mostly for research or triage |
| Auditability and Logging | Complete control over logs, engine updates, and workflow compliance | Limited; dependent on provider’s reporting policies |
| Infrastructure Dependency | On-prem, predictable performance; no internet required | Cloud-based, requires connectivity; variable performance |
| Cost Structure | Fixed subscription + engine licenses; predictable enterprise cost | Pay-per-scan or subscription; costs scale with volume |
| Best Use Case | Regulated environments (banks, financial services, government), inline scanning, compliance workflows | Threat research, malware triage, low-sensitivity analysis |
Contact us to arrange a technical briefing, request a proof-of-concept deployment, or discuss commercial terms.